概述
日期
2024年05月15日
09:00 - 10:00
所在
运动行、Bilibili

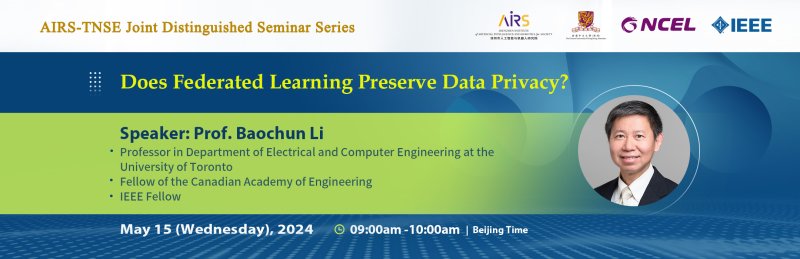
Does Federated Learning Preserve Data Privacy?

首页- 优德官网集团(中国)有限公司


近五年来,,,,, , ,,联邦学习风行学界,,,,, , ,,其特点之一是可以为数据隐私提供保唬;;;;ぁ。。 。。。 。可是有研究对其数据隐私保唬;;;;さ哪芰μ岢隽艘晌剩,,,, , ,,并提出可以使用梯度泄露攻击来重修训练数据。。。 。。。 。然而,,,,, , ,,在Plato平台举行的用联邦学习解决图像分类和自然语言处置惩罚使命等实验证实晰梯度泄露攻击的说法并不建设,,,,, , ,,联邦学习中的数据隐私现实上获得了很好的保唬;;;;ぁ。。 。。。 。

第十四期优德官网-TNSE团结优异讲座系列运动,,,,, , ,,我们有幸约请到李葆春教授先容联邦学习的数据隐私保唬;;;;つ芰Γ,,,, , ,,并分享他在这个领域内的相关研究效果与有趣发明。。。 。。。 。

优德官网-TNSE Joint Distinguished Seminar Series is co-sponsored by IEEE Transactions on Network Science and Engineering (TNSE) and Shenzhen Institute of Artificial Intelligence and Robotics for Society (优德官网), with joint support from The Chinese University of Hong Kong, Shenzhen, Network Communication and Economics Laboratory (NCEL), and IEEE. This series aims to bring together top international experts and scholars in the field of network science and engineering to share cutting-edge scientific and technological achievements.

Join the seminar through Bilibili (http://live.bilibili.com/22587709).

  • 首页- 优德官网集团(中国)有限公司
    Jianwei Huang
    Vice President, 优德官网; Presidential Chair Professor, CUHK-Shenzhen; Editor-in-Chief, IEEE TNSE; IEEE Fellow; AAIA Fellow
    Executive Chair
  • 首页- 优德官网集团(中国)有限公司
    Baochun Li
    Professor in Department of Electrical and computer Engineering at theUniversity of Toronto; Fellow of the Canadian Academy of Engineering; IEEE Fellow
    Does Federated Learning Preserve Data Privacy?

    李葆春教授于1995年从中国清华大学盘算机科学与手艺系获得工学学士学位,,,,, , ,,随后于1997年和2000年划分在伊利诺伊大学厄巴纳-香槟分校的盘算机科学系获得硕士和博士学位。。。 。。。 。自2000年起,,,,, , ,,他一直在多伦多大学的电子与盘算机工程系任职,,,,, , ,,现在是该系的教授。。。 。。。 。自2005年8月以来,,,,, , ,,他担当贝尔加拿大盘算机工程讲席教授。。。 。。。 。他现在的研究兴趣包括云盘算、清静与隐私、漫衍式机械学习、联邦学习和网络手艺。。。 。。。 。

    李博士揭晓了共计470余篇论文,,,,, , ,,累积引用量达25000,,,,, , ,,H-index指数为88,,,,, , ,,i10-index指数为338。。。 。。。 。他曾在2000年获得IEEE通讯学会Leonard G. Abraham通讯辖档挽域奖,,,,, , ,,2009年获得IEEE通讯学会多媒体通讯最佳论文奖,,,,, , ,,同年还获得了多伦多大学McLean奖。。。 。。。 。他在2023年获得了IEEE INFOCOM最佳论文奖,,,,, , ,,并在2024年获得了IEEE INFOCOM成绩奖。。。 。。。 。同时,,,,, , ,,他是加拿大工程院院士、加拿大工程学会院士以及国际电气与电子工程师协会会士(IEEE Fellow)。。。 。。。 。

    As one of the practical paradigms that preserves data privacy when training a shared machine learning model in a decentralized fashion, federated learning has been studied extensively in the past five years. However, a substantial amount of existing work in the literature questioned its core claim of preserving data privacy, and proposed gradient leakage attacks to reconstruct raw data used for training. In the day and age of fine-tuning large language models, whether data privacy can be preserved is very important. 

    In this talk, I will show that despite the conventional wisdom that federated learning pose privacy leaks, data privacy, in fact, may be quite well protected.  Claims in the existing literature on gradient leakage attacks are not valid in our experiments, for both image classification and natural language tasks. Our extensive array of experiments were based on Plato, an open-source framework that I developed from scratch for reproducible benchmarking comparisons in federated learning.